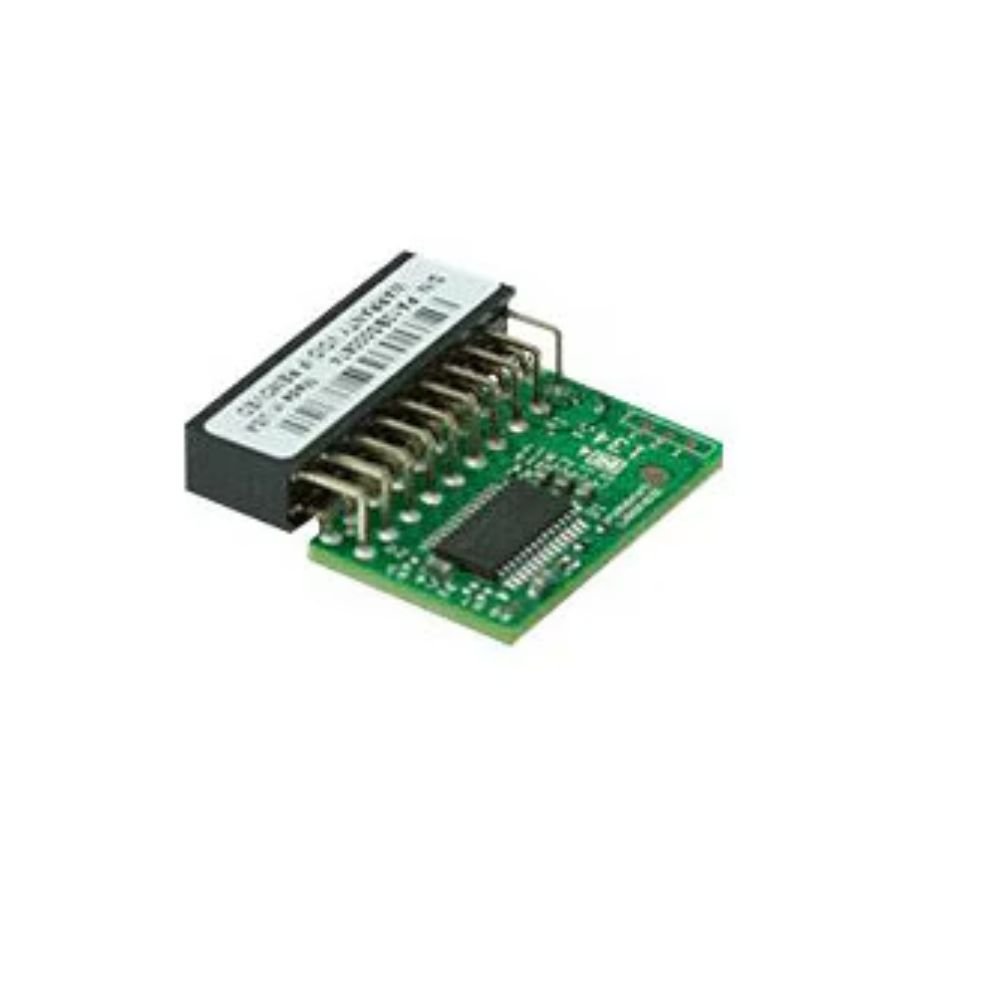
This TPM 2.0 Trusted Platform Module is designed to provide hardware-based security features for compatible computer systems. It includes an Endorsement Key, Intel Trusted Execution Technology support, Memory Encryption/Decryption, protection against dictionary attacks, over/under voltage detection, reset filtering, and a tick counter with tamper detection. The module also features high- and low-frequency sensors and a True Random Number Generator for enhanced security functionality. Its vertical orientation supports convenient installation in compatible systems. The black and green module measures 1 inch in height, 0.3 inch in width, and 1 inch in depth. It is supplied as one unit and does not require service activation.
Copyright 2026 ©inprocure.ai. All rights reserved.